Gideon Jose runs production data center infrastructure and is finishing a degree in Data Networking and Security.
I graduate from Liberty University in spring 2028 with a B.S. in Information Technology. My work spans servers, networks and security: I build, migrate, address and protect production systems, and I log every task and every lab. This site is that record.
What happens to a server after it leaves the loading dock.
Every application a company runs lives on a machine somebody had to mount, cable, address, configure and protect. That somebody is me. Here is the job in six steps.
Step 01 · Rack mount
It arrives
A new server comes off the pallet. I fit the rails, seat it in the rack and check it against the build sheet before anything gets power. On one delivery that meant 30 servers at a single site.
Step 02 · Switches and cabling
It gets connected
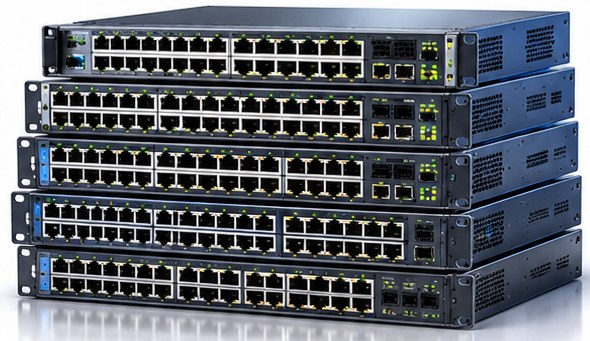
I find free switch ports, record the switch, port, speed and cable type on the cabling sheet, then run the management and data cables. A server nobody can reach is furniture.
Step 03 · IP address administration
It gets an address
I reserve the management address in IPAM. Once, an address listed as free was already in use by a device nobody had registered. I traced it, documented it and got a clean one assigned.
Step 04 · Blade and rack servers
It gets an identity
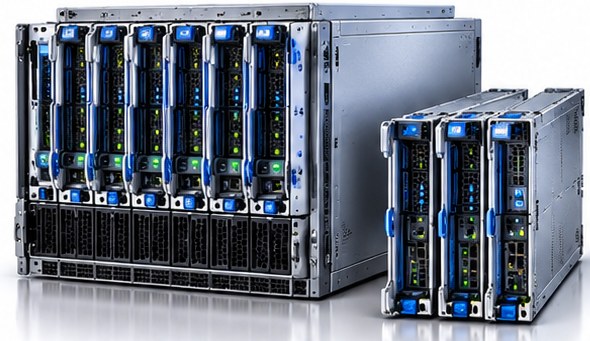
Each week I migrate Cisco UCS blades from the old domain to a new Fabric Interconnect domain, and I move local service profiles to global in UCS Central. On Lenovo I set up the management controller. When a blade faults, I find the bad part and replace it.
Step 05 · Security
It gets protected
I turn on drive encryption across the server fleet and work in an environment fronted by Palo Alto firewalls and F5 load balancers. In the lab I take a vulnerability scan from finding to verified patch.
NOVEMBER 2026 duplicate IP traced, new address requested
NOVEMBER 2026 domain controller build started
OCTOBER 2026 service profiles globalized
OCTOBER 2026 WSUS patch lab verified
▮ next entry
Step 06 · Documentation
It gets written down
Every job ends as a log entry, so the next person knows what was done and why. The full log is below, and it grows every week.
Weekly migrations to a new domain, fault diagnosis and DIMM replacement.
Switches
Port mapping and cabling for every new build.
Core routers
Part of the production network I support every day.
Firewall
Part of the production network I support every day.
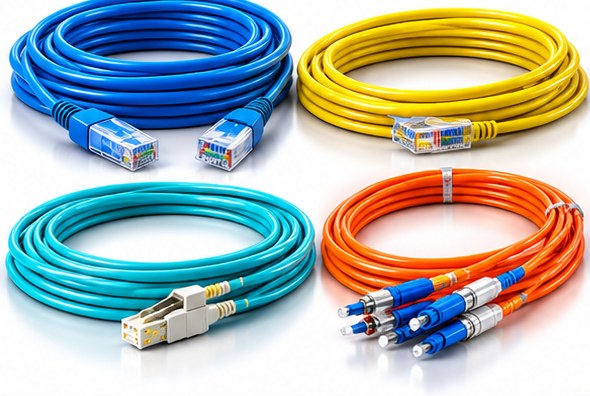
Cables
Copper and fiber runs, each recorded on the cabling sheet.
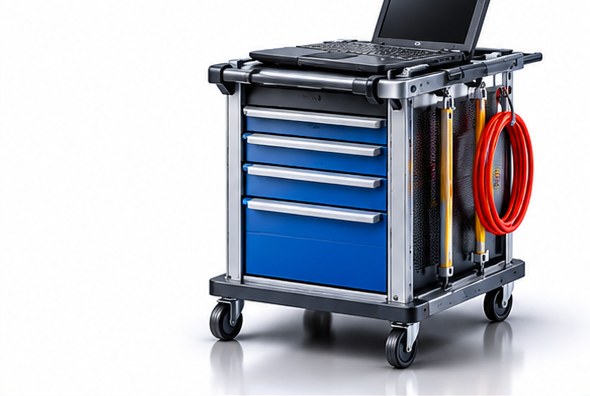
Crash cart
Console access at the rack when a server will not answer remotely.
01
Experience
Data Center Technician
Apr 2026 to present
Genworth Financial, Lynchburg, VA (contract through Randstad)
Install, cable and bring online Cisco UCS and Lenovo ThinkSystem servers across multiple data center sites, including a 30-server delivery.
Troubleshoot hardware faults on UCS blades and rack servers: DIMM replacements, RAID controller and drive migrations, POST and fault LED issues.
Migrate Cisco UCS blades from the old domain to a new Fabric Interconnect domain in weekly batches.
Manage service profiles in Cisco UCS Central, including moving local profiles to global.
Reserve management IPs in Infoblox IPAM and locate free switch ports with AKiPS for new builds.
Build Lenovo SR650 V4 servers as additional domain controllers and roll out XClarity drive encryption across the Lenovo fleet.
Took part in a 500-unit hardware end-of-life retirement project.
02
Work log
Tasks from the job and labs from Liberty University. Newest first.
Ongoing
Migration
Blade migrations to a new Fabric Interconnect domain
An ongoing project: moving Cisco UCS blades out of the old UCS domain and into a new Fabric Interconnect domain, a batch each week.
November 2026
Troubleshooting
Traced an unreachable management interface to a duplicate IP
A new server's management controller would not respond. The address I had reserved showed as free in IPAM, but an unregistered storage node on another switch was already using it. I documented the conflict and requested a new address and port.
Build
Two Lenovo SR650 V4 servers as additional domain controllers
Started from bare hardware: XCC configuration in XClarity Provisioning Manager, then preparing both machines to join the existing domain as controllers.
Security
Drive encryption rollout on the Lenovo fleet
Enabling XClarity-managed drive encryption across the company's Lenovo servers.
October 2026
Configuration
Globalized local service profiles in Cisco UCS Central
Ran the evaluate step, resolved what it flagged, then started globalization so the profiles are managed centrally.
Build
Cabled new Lenovo ThinkSystem servers for two sites
Found free switch ports in AKiPS, completed the cabling sheet with switch, port, speed and cable type, connected the XCC and OCP NIC ports, and reserved the management addresses in Infoblox.
Liberty lab
WSUS patching from vulnerability scan to verified fix
CSIS 341 lab. Identified missing updates from MBSA and OpenVAS reports, approved them in WSUS, installed them on the Windows client and verified the result.
September 2026
Hardware
Moved a UCS C240 M4 RAID controller and drives into a new chassis
Migrated the controller and drive set, then worked through POST and system fault LED issues until the server came up clean.
Earlier in 2026
Build
Installed 30 Lenovo servers at a second data center
Travelled on-site to rack and install a 30-server delivery.
Hardware
Replaced a DIMM in a Cisco UCS B200 M5 blade
Owned the job from start to finish and wrote it up in the operations journal.
Troubleshooting
FRU retrieval error on a UCS blade
Worked a blade that was reporting an inventory retrieval fault in its chassis.
Lifecycle
Hardware refresh and a 500-unit retirement project
Replaced an aging Cisco C240 with a new UCS server, and travelled to another site to help retire 500 end-of-life units.
Troubleshooting
Stale DNS record behind an unreachable UCS Manager GUI
The management GUI for one UCS domain stopped loading. The cause was an outdated DNS record, which I identified and had corrected.
Security
Caught and reported a delivery-notice phishing email
The message claimed a pending delivery I was not expecting and the sender did not match the carrier. I checked the tracking number on the carrier's own site instead of the link, it came back invalid, and I reported it.
03
Skills and know-how
Each one names where I have done it.
Infrastructure operations
Weekly blade migrations to a new Fabric Interconnect domain, hardware refresh and end-of-life retirement, fault diagnosis, and a written record of every change.
Where: On the job
Servers and compute
Rack, cable and bring up Cisco UCS blade and rack servers and Lenovo ThinkSystem servers. UCS Manager, UCS Central and XClarity. DIMM, RAID controller and drive work.
Where: On the job
Networking
Switch port mapping and structured copper and fiber cabling, IP address management in Infoblox, and troubleshooting DNS and duplicate-IP faults in a Palo Alto and F5 environment.
Where: On the job · CCNA
Vulnerability and patch management
Read OpenVAS and MBSA scan results, decide what is missing, deploy the updates through WSUS and confirm the fix on the client.
Where: Liberty lab
Threat detection
Spot and report phishing, triage processes, services and logs with PowerShell, and investigate suspicious infrastructure with OSINT.
Where: On the job · Home lab
Systems and data protection
Build Windows Server domain controllers and roll out drive encryption across a server fleet.
Where: On the job · Security+
04
Credentials
CompTIA Security+
DoD 8570 compliant
Active
Cisco CCNA
Routing, switching and network fundamentals
Active
CompTIA CySA+
Studying now
Exam planned September 2027
B.S. Information Technology, Data Networking and Security
Liberty University. Member, Omega Nu Lambda National Honor Society, Alpha Chapter.
Expected spring 2028
05
Home lab
Outside work I run a weekly security lab and publish the write-ups. Each weekend follows the same pattern: learn something, practice it, document it.
PowerShell SOC triage series covering basics, process monitoring, services and logs.
OSINT investigations, including Tor exit nodes and bulletproof hosting IPs.
TryHackMe and Hack The Box on alternating weeks, with SOC Level 1 phishing analysis in progress.
I volunteer each October with the cleanup crew for the Appomattox County Railroad Festival, and during the COVID-19 pandemic I helped with meal distribution for people without housing.
Building out an infrastructure, network or security team? I would like to hear about it.